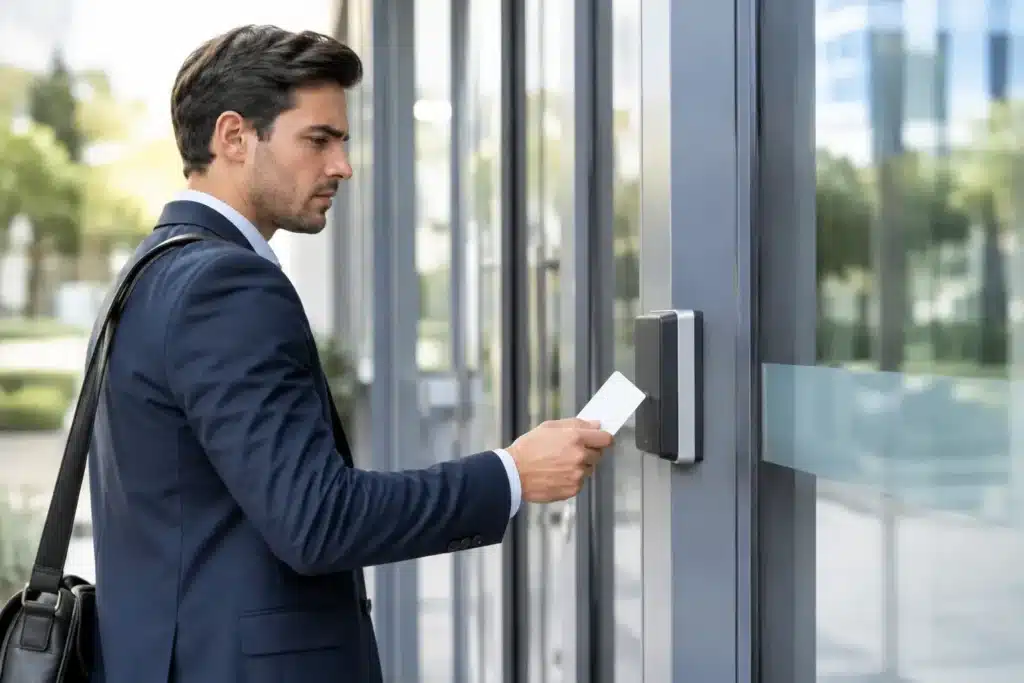
An employee who left three months ago can still enter a warehouse. A delivery driver is issued a shared card with no expiry date. A server-room door is released remotely without anyone confirming who requested it. These are not minor administrative gaps. Access control failures create direct exposure to theft, unauthorized access, safety incidents, and compliance issues.
For facilities that manage valuable stock, sensitive information, restricted areas, or large workforces, access control must do more than open doors. It must show who entered, when they entered, which areas they could access, and whether the system is operating as approved. When that chain breaks, the security risk grows quickly.
What Access Control Failures Look Like in Practice
Many failures are not caused by a broken reader or a damaged door lock. They start with weak operating processes. Credentials are issued without a documented approval path, access rights are copied from a previous employee, or temporary users remain active after their work is complete.
A system may also be technically installed but poorly configured. Doors can be assigned incorrect schedules, anti-passback rules may be disabled, or high-risk areas may have the same access profile as general office space. In a multi-tenant building, this can allow contractors, visitors, or former occupants into areas they should never reach.
Physical hardware matters as well. A misaligned magnetic lock, loose door contact, failing backup battery, or unprotected exit button can undermine an otherwise well-designed system. If a door is shown as closed in the software but is physically unsecured, the site has a false sense of protection.
The most serious failures often occur when these issues overlap: weak credential management, unreliable hardware, and no regular review of event logs. A security incident then becomes difficult to investigate because the available records are incomplete or inaccurate.
The Operational Cost of Poor Access Control
Unauthorized entry is the most obvious concern, but it is not the only one. Access control failures can interrupt daily operations. A warehouse team may be unable to enter loading areas during a shift change. Hotel staff may lose access to service corridors. A facility manager may need to manually override doors during a system outage, removing the audit trail at the exact moment it is needed.
For property developers, building operators, and contractors, these problems can also delay handover. Security systems are often reviewed alongside CCTV, fire and life-safety interfaces, and other ELV infrastructure. If door hardware, drawings, access levels, and system reports do not match the approved design, corrective work can affect project timelines and approval schedules.
There is also a people-management issue. When staff see that cards are routinely shared or doors are routinely propped open, they receive a clear message: security procedures are optional. That behavior is difficult to reverse after it becomes normal practice.
Common Causes of Access Control Failures
Access Rights Are Not Managed Through the Employee Lifecycle
Every organization needs a defined process for onboarding, role changes, leave, and termination. Access should be based on job function, location, and working hours, not convenience. A finance employee does not require access to a maintenance room, and a contractor working a weekend shift does not need permanent 24-hour entry.
Termination is especially time-sensitive. Credentials, mobile access permissions, PIN codes, remote platform accounts, and keys must be disabled or recovered immediately. Delays create an avoidable risk window.
System Design Does Not Match Site Operations
A small office and a logistics hub should not use the same access strategy. Warehouses may need separate permissions for loading bays, high-value storage, control rooms, and staff accommodation. Healthcare facilities may need stricter control around medication, records, and equipment rooms. Retail locations may require controlled back-of-house access while keeping customer circulation simple.
The right design depends on traffic flow, emergency egress requirements, operating hours, staffing patterns, and the assets being protected. Overly restrictive systems slow operations. Overly broad permissions weaken security. The objective is controlled access without creating unnecessary friction for authorized users.
Installation and Integration Gaps
Access control is not only software and card readers. It includes locks, door contacts, request-to-exit devices, emergency break-glass units, cabling, power supplies, network connectivity, and backup power. Each component must be selected and installed correctly.
Integration adds another layer. CCTV verification can help security teams review door events. Visitor management can support temporary credential control. Fire alarm interfaces may be required to release designated doors during an emergency. These integrations must be tested under real operating conditions, not assumed to work because devices are connected.
No Testing, Maintenance, or Audit Discipline
A door may operate normally for months while its event reporting, battery backup, or alarm monitoring is not functioning correctly. Without planned testing, the first sign of failure may be during an incident or inspection.
Regular maintenance should confirm that doors lock and release as intended, contacts report accurately, controllers communicate with the platform, and access reports can be retrieved. It should also include a review of inactive cards, duplicate credentials, expired visitors, forced-door alarms, and repeated access-denied events.
How to Prevent Access Control Failures
Prevention starts before equipment is ordered. A site survey should identify entry points, restricted zones, user groups, emergency routes, existing infrastructure, and authority requirements. The system design can then define which doors require access control, what credential method is suitable, and how activity will be monitored.
Use role-based access profiles rather than issuing permissions door by door whenever possible. This makes it easier to apply consistent rules for employees, managers, security personnel, contractors, and visitors. It also makes audits faster because access can be reviewed by role and department.
Establish clear ownership. Human resources or management should notify the responsible administrator when staff join, change roles, or leave. Security teams should have a process for approving exceptions. Facility managers should know who is responsible for responding to door alarms, equipment faults, and forced-entry events.
For larger or higher-risk sites, consider layered controls. A card alone may be suitable for low-risk internal areas, while server rooms, cash offices, jewelry storage, or critical infrastructure may require a PIN, biometric verification, or security desk approval. The right level of control depends on the risk, the number of users, and the operational impact of a delay.
Compliance Requires More Than Installed Equipment
In compliance-driven projects, a working access control system is only part of the requirement. Documentation, approved equipment where applicable, installation quality, testing records, drawings, and handover procedures can all affect whether a project is accepted without rework.
Dubai, Abu Dhabi, and Sharjah facilities may have different authority expectations depending on the sector, building type, and scope of security work. A contractor that understands local compliance requirements can identify issues early, coordinate the correct system design, and reduce the chance of costly changes late in the project.
ALNAJAH ALAWAL SECURITY SYSTEMS & EQUIPMENT TRADING L.L.C. approaches access control as an operational and compliance system, not a collection of devices. Proper surveys, coordinated installation, testing, commissioning, staff training, and maintenance support help clients maintain control after handover, not only on installation day.
When to Review Your Existing System
Do not wait for a theft, unauthorized entry, or failed inspection. Review access control after a move, expansion, tenant change, major staffing shift, security incident, or renovation. These events often create new doors, new user groups, and new risks that the original configuration does not address.
A review is also warranted when users rely on shared cards, physical keys are filling gaps in the electronic system, doors are regularly left open, or management cannot quickly produce a reliable access report. These are signs that the system no longer reflects how the facility operates.
The most effective access control strategy is practical: give authorized people the access they need, deny access where it creates risk, and keep a dependable record of every decision. Stay compliant. Stay protected.